Skip to content
Smart Lead Tech
Home
Services
Our work
Saudi Arabia
About us
Blog
Contact us
🇸🇦العربيةContact now
Smart Lead Tech

Smart software solutions

Follow us

Company

  • About us
  • Our work
  • Our services
  • Saudi Arabia
  • Restaurant POS
  • Contact us
  • Book a call

Quick links

  • Blogs
  • Pricing
  • Refund policy
  • Privacy policy
  • Terms and conditions
  • Data deletion

Contact us

  • Egypt — Head Office

    Office 6, Bldg 23, Makkah Al-Mukarramah St., Omraneya, Giza 3540203, Egypt
  • Saudi Arabia — Branch

    Bldg 2646, Secondary 123, Street 7697, Ishbiliyah Dist., Jubail 35416, Kingdom of Saudi Arabia
  • Email address

    help@smartleadtech.com
  • Phone number 🇪🇬

    +20 102 201 4671
  • Phone number 🇸🇦

    +966 53 044 7112

© 2026 Smart Lead Tech. All rights reserved.

  • Smart Lead Tech Information Technology LLC·Commercial Register ⁦61239⁩·Tax ID ⁦774-391-316⁩

  • Smart Lead Tech Software Establishment·CR ⁦7054902585⁩·VAT

Q&A: can AI test your app and scan its security instead of your team?

We get these questions every week from clients and engineers. Here are our straight answers, based on what we actually run in Security Guard Scanner, CyberBattleGround, Splunk Log Viewer and HTM‑Drive. Does AI write UI t…
12/16/2025 — 7 min read

An automated browser testing a web page with security-scan results beside it

We get these questions every week from clients and engineers. Here are our straight answers, based on what we actually run in Security Guard Scanner, CyberBattleGround, Splunk Log Viewer and HTM‑Drive.

Does AI write UI tests instead of the engineer?

It writes the draft, yes — impressively fast. We give it the feature description and the user path, and it produces Playwright tests covering the basic cases. But the tests that catch real bugs are the ones the engineer adds: what happens when the network drops mid-payment, or when the user taps twice. AI widens coverage; the human aims it at what hurts.

Can it find vulnerabilities?

Security Guard Scanner detects XSS, SQLi, CSRF and server-side weaknesses automatically, and that predates the LLM wave. What models added: reading the code, not just hammering the interface. The model suggests “this route builds the query by string concatenation, try this input”, so scanning becomes guided rather than blind. Result: more findings with less noise.

The scanner says “vulnerability here”. The model says “vulnerability here, this is why, and this is the fix”. The difference is hours of engineering time per finding.

Can the fixes it proposes be trusted?

No — not without testing. On CyberBattleGround (a training arena for breaking deliberately vulnerable apps) we tried generated fixes: some closed the hole and opened another. A fix is merged only after the original exploit fails and the full suite passes. The model accelerates; the test decides.

What about logs? Does AI read millions of lines?

Here it truly shines. Splunk Log Viewer ingests logs and provides advanced search; on top of it, a model layer explains anomalies in Arabic: “spike in failed logins from one IP range within 10 minutes — looks like credential guessing”. The analyst reads a sentence instead of a thousand lines, and decides.

Does it protect our data in cloud storage?

HTM‑Drive (cloud storage integrated with OneDrive) uses a model to classify sensitive files on upload (ID, contract, financial data) and automatically apply a stricter sharing policy. AI does not “protect”; it classifies, and the policy protects.

What should never be delegated?

  • The release decision.
  • Judging “is this vulnerability critical for our business?” — the business knows what matters to it.
  • Notifying a client or regulator about an incident.

So do we still need a QA and security team?

You need a smaller team that thinks more and types less. AI removed the “typing”; it did not remove “thinking about what could happen”. That was always the hard part.
Share

Projects related to this article

  • CybersecurityNext.js

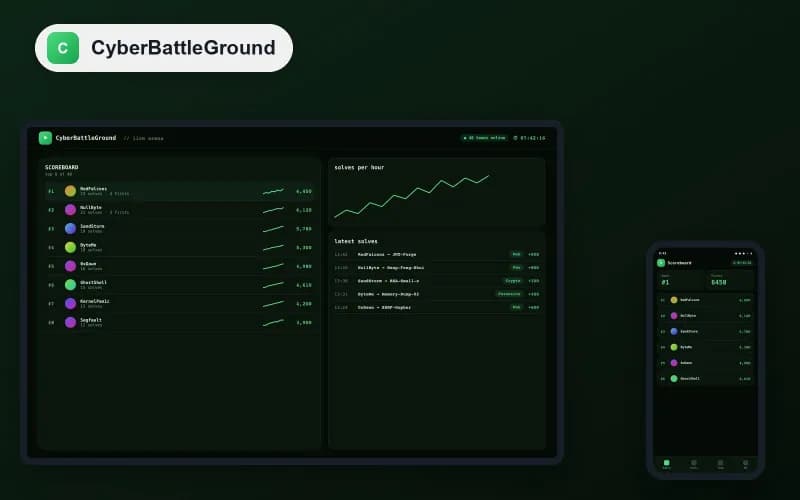
    CyberBattleGround — Capture-The-Flag Platform

    A full Capture-The-Flag arena for training cybersecurity teams and stress-testing vulnerability-discovery skills inside an isolated virtual environment.

    Show more
    CyberBattleGround security platform — live leaderboard
  • CybersecurityLaravel

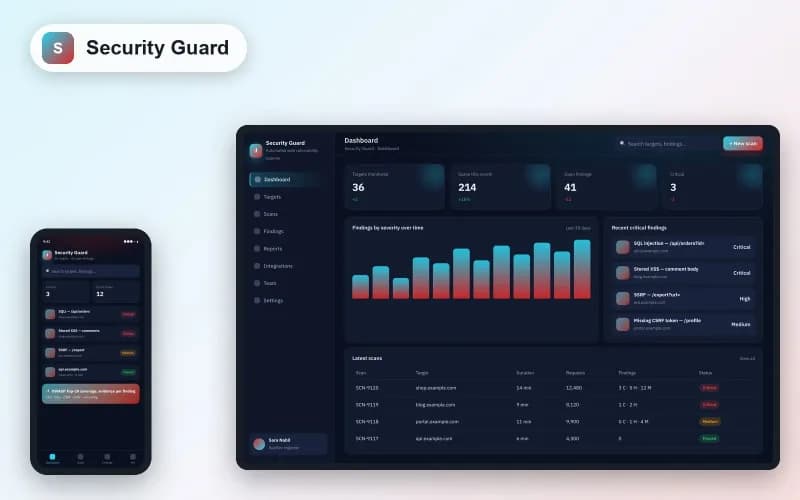
    Security Guard Scanner — Automated Web Vulnerability Scanner

    An end-to-end web vulnerability scanner that detects XSS, SQLi, CSRF and server-side weaknesses automatically — with downloadable, audit-ready reports.

    Show more
    Security Guard Scanner — automated vulnerability report
  • CybersecurityLaravel

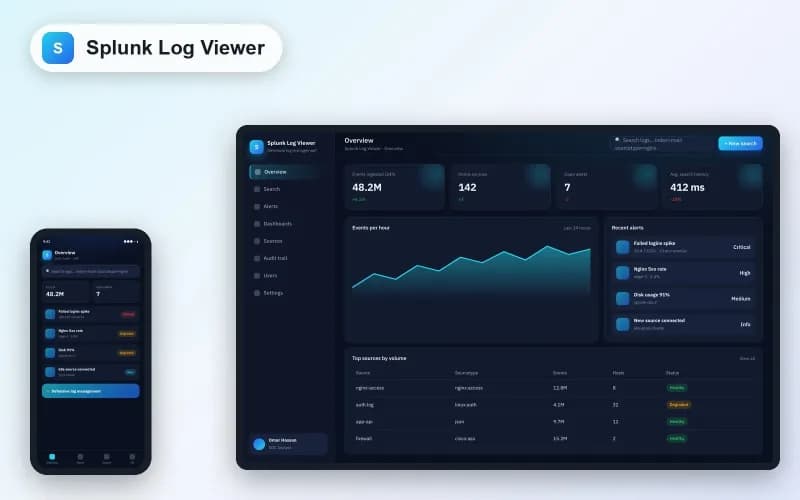
    Splunk Log Viewer — Defensive Log Management & Analysis

    A defensive web app that integrates Laravel with Splunk for log ingestion, advanced search, and audit-ready storage of investigation results.

    Show more
    Splunk Log Viewer dashboard — security log analysis

Related Blogs

  • Diverse tech team collaborating in an innovative AI-powered environment in the GCC and Egypt.

    GCC & Egypt Tech Talent Market: Strategies for Building Future-Ready Teams in the AI Era

    The tech job market in the GCC and Egypt is undergoing rapid transformations, driven by massive government investments in digital transformation and AI, alongside global shifts towards a knowledge economy. These changes …

    10/09/2026 — 8 min read

  • A server inside a local data centre with a lock icon and the Saudi flag

    AI inside your walls: a PDPL compliance guide that does not stall the project

    The question that precedes any AI contract with a Saudi organisation today is not “how accurate?” but “where does our data go?”. The Personal Data Protection Law (PDPL) turned that worry into a legal obligation. This gui…

    05/05/2026 — 10 min read

  • DevSecOps pipeline

    DevSecOps for startups: the non-negotiable baseline

    Security at startups is usually postponed until the first incident. The list below is what we apply on day one at Smart Lead Tech in every project — small or large — and it costs the team almost no time.1. Secret hygiene…

    09/03/2024 — 12 min read