Skip to content
Smart Lead Tech
Home
Services
Our work
Saudi Arabia
About us
Blog
Contact us
🇸🇦العربيةContact now
Smart Lead Tech

Smart software solutions

Follow us

Company

  • About us
  • Our work
  • Our services
  • Saudi Arabia
  • Restaurant POS
  • Contact us
  • Book a call

Quick links

  • Blogs
  • Pricing
  • Refund policy
  • Privacy policy
  • Terms and conditions
  • Data deletion

Contact us

  • Egypt — Head Office

    Office 6, Bldg 23, Makkah Al-Mukarramah St., Omraneya, Giza 3540203, Egypt
  • Saudi Arabia — Branch

    Bldg 2646, Secondary 123, Street 7697, Ishbiliyah Dist., Jubail 35416, Kingdom of Saudi Arabia
  • Email address

    help@smartleadtech.com
  • Phone number 🇪🇬

    +20 102 201 4671
  • Phone number 🇸🇦

    +966 53 044 7112

© 2026 Smart Lead Tech. All rights reserved.

  • Smart Lead Tech Information Technology LLC·Commercial Register ⁦61239⁩·Tax ID ⁦774-391-316⁩

  • Smart Lead Tech Software Establishment·CR ⁦7054902585⁩·VAT

DevSecOps for startups: the non-negotiable baseline

Security at startups is usually postponed until the first incident. The list below is what we apply on day one at Smart Lead Tech in every project — small or large — and it costs the team almost no time.1. Secret hygiene…
09/03/2024 — 12 min read

DevSecOps pipeline

Security at startups is usually postponed until the first incident. The list below is what we apply on day one at Smart Lead Tech in every project — small or large — and it costs the team almost no time.

1. Secret hygiene

  • No secrets in the repo. Ever. We use Doppler/1Password + pre-push git hooks.
  • Rotate shared keys at least every 90 days.
  • Run gitleaks on every PR in CI.

2. SCA (trusted dependencies)

Every repo has dependabot + npm audit / composer audit in CI. Critical alerts auto-open issues rather than waiting for a developer.

3. SAST + Lint

  • PHP: PHPStan level 6 + Pint.
  • TypeScript: ESLint security plugin + tsc --noEmit.
  • Docker: hadolint + trivy image scan.

4. OWASP ASVS — Level 2 as the floor

ASVS Level 2 is not "for big companies" — it is the pragmatic floor for any product touching real user data. Block one day each quarter for a review.

We focus on: authn/authz, encryption in transit & at rest, audit logs, and strict rate limits on every API.

5. Runtime

  • Security headers via middleware (Next.js + Laravel).
  • Per-request CSP with a nonce.
  • A small WAF (Cloudflare) locks out bots from day one.

6. DR + backups

Daily encrypted backups + a monthly restore drill. A project that has never tested a restore does not have backups — it has an illusion.

Takeaway

DevSecOps is not a separate budget; it is a habit layer. Adopt it on day one and you will pay a tiny premium to avoid incident bills that can end the whole company.
Share

Projects related to this article

  • CybersecurityNext.js

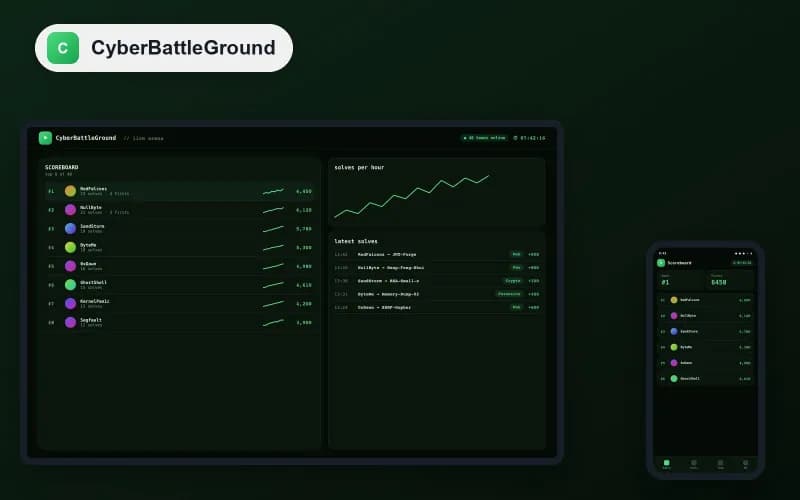
    CyberBattleGround — Capture-The-Flag Platform

    A full Capture-The-Flag arena for training cybersecurity teams and stress-testing vulnerability-discovery skills inside an isolated virtual environment.

    Show more
    CyberBattleGround security platform — live leaderboard
  • CybersecurityLaravel

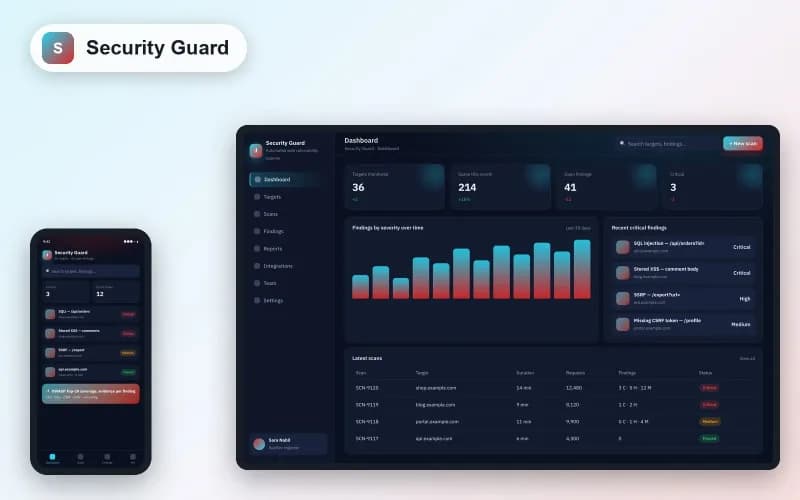
    Security Guard Scanner — Automated Web Vulnerability Scanner

    An end-to-end web vulnerability scanner that detects XSS, SQLi, CSRF and server-side weaknesses automatically — with downloadable, audit-ready reports.

    Show more
    Security Guard Scanner — automated vulnerability report
  • CybersecurityLaravel

    Splunk Log Viewer — Defensive Log Management & Analysis

    A defensive web app that integrates Laravel with Splunk for log ingestion, advanced search, and audit-ready storage of investigation results.

    Show more
    Splunk Log Viewer dashboard — security log analysis

Related Blogs

  • Illustrative image of a digital roadmap combining FinTech and compliance elements in the GCC and Egypt region

    FinTech and Digital Compliance: A Founder's Roadmap for a Transformative Quarter in GCC and Egypt

    The digital landscape in the GCC and Egypt is accelerating rapidly, driven by supportive regulations, infrastructure investments, and clear trends towards innovation and financial inclusion. As entrepreneurs and startup …

    10/19/2026 — 7 min read

  • Startup founder reviewing cybersecurity and compliance reports on a computer screen in a modern office.

    Cybersecurity and Data Protection Tighten in GCC and Egypt: Insights for Founders

    In the face of escalating digital challenges, cybersecurity is no longer just a technological option; it has become a fundamental pillar for business continuity and regulatory compliance. The digital landscape in the GCC…

    09/17/2026 — 10 min read

  • An automated browser testing a web page with security-scan results beside it

    Q&A: can AI test your app and scan its security instead of your team?

    We get these questions every week from clients and engineers. Here are our straight answers, based on what we actually run in Security Guard Scanner, CyberBattleGround, Splunk Log Viewer and HTM‑Drive. Does AI write UI t…

    12/16/2025 — 7 min read