Skip to content
Smart Lead Tech
Home
Services
Our work
Saudi Arabia
About us
Blog
Contact us
🇸🇦العربيةContact now
Smart Lead Tech

Smart software solutions

Follow us

Company

  • About us
  • Our work
  • Our services
  • Saudi Arabia
  • Restaurant POS
  • Contact us
  • Book a call

Quick links

  • Blogs
  • Pricing
  • Refund policy
  • Privacy policy
  • Terms and conditions
  • Data deletion

Contact us

  • Egypt — Head Office

    Office 6, Bldg 23, Makkah Al-Mukarramah St., Omraneya, Giza 3540203, Egypt
  • Saudi Arabia — Branch

    Bldg 2646, Secondary 123, Street 7697, Ishbiliyah Dist., Jubail 35416, Kingdom of Saudi Arabia
  • Email address

    help@smartleadtech.com
  • Phone number 🇪🇬

    +20 102 201 4671
  • Phone number 🇸🇦

    +966 53 044 7112

© 2026 Smart Lead Tech. All rights reserved.

  • Smart Lead Tech Information Technology LLC·Commercial Register ⁦61239⁩·Tax ID ⁦774-391-316⁩

  • Smart Lead Tech Software Establishment·CR ⁦7054902585⁩·VAT

All projects
CybersecurityLaravel

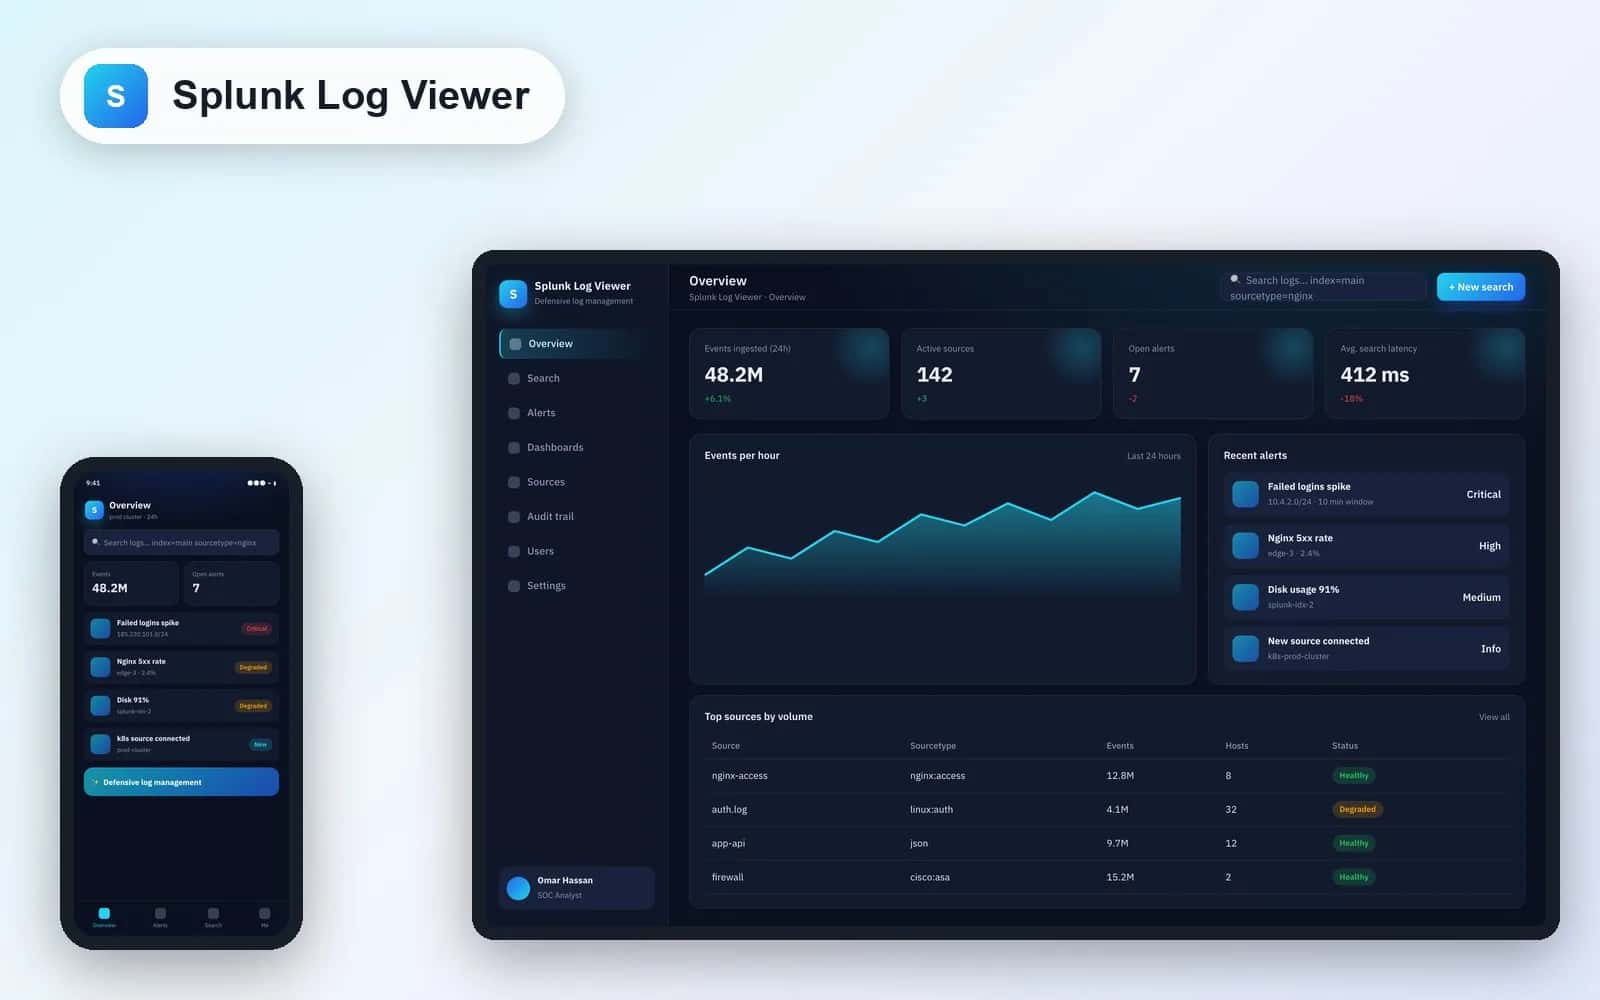
Splunk Log Viewer — Defensive Log Management & Analysis

A defensive web app that integrates Laravel with Splunk for log ingestion, advanced search, and audit-ready storage of investigation results.

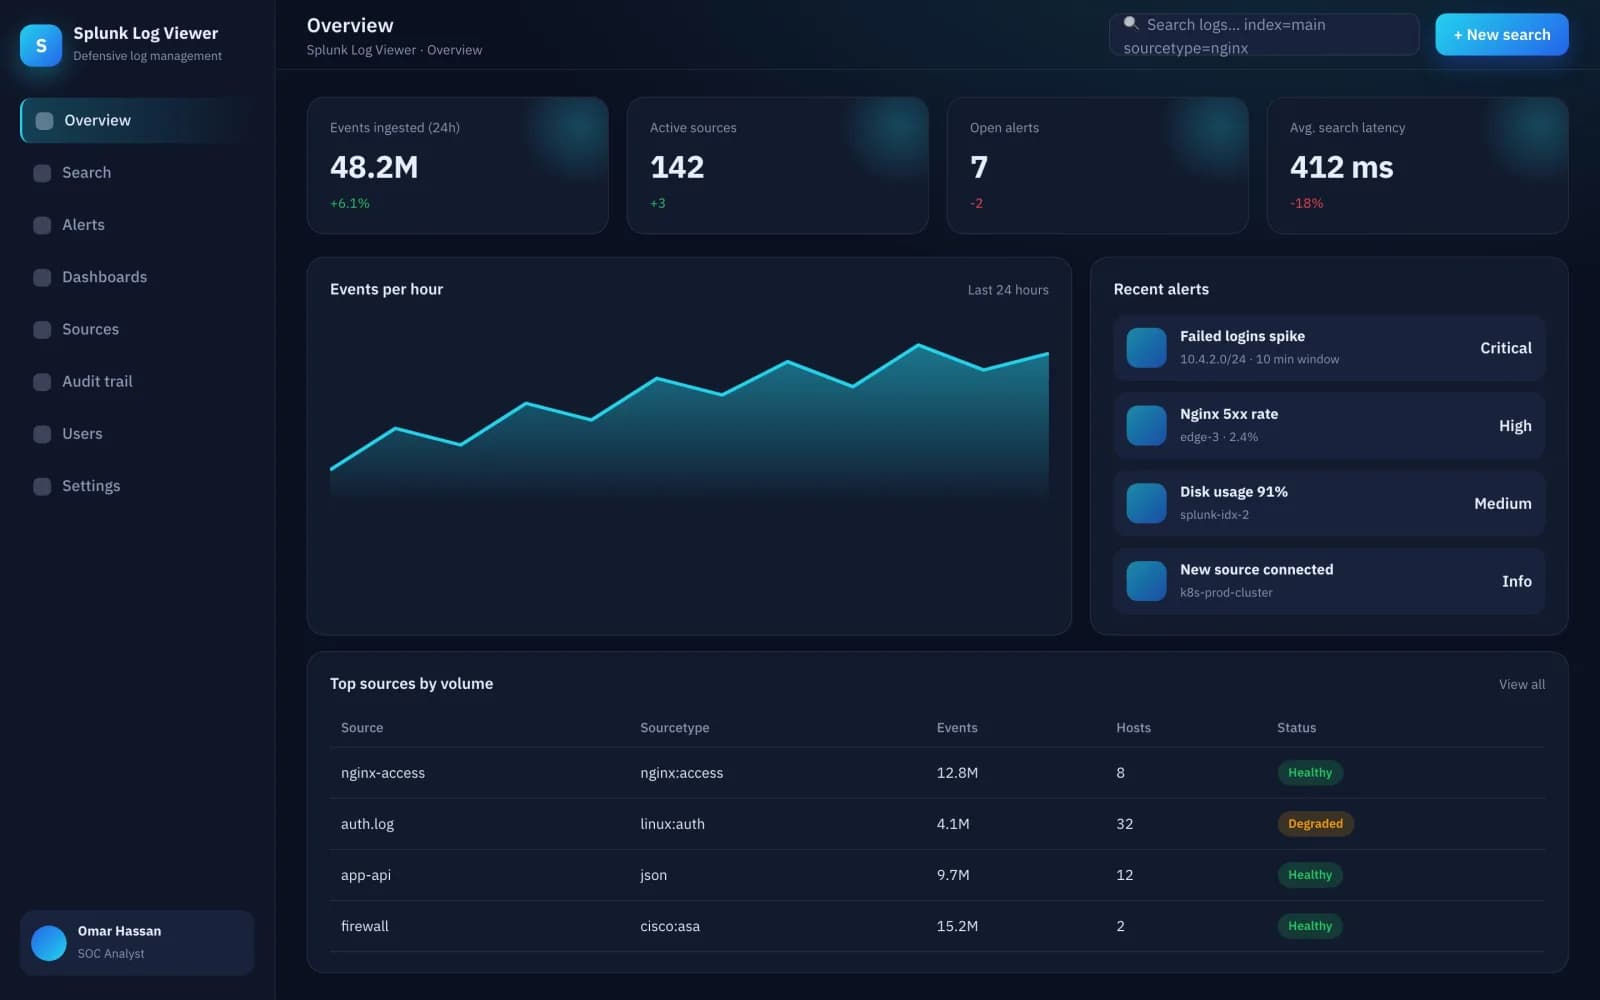
Splunk Log Viewer dashboard — security log analysis
Client
Smart Lead Tech — Blue Team Lab
Launched
22 January 2024

Project at a glance

The Smart Lead Tech security guild built this defensive (Blue Team) tool to help SOC analysts ingest, query and store logs from diverse sources — web servers, firewalls, endpoints, and cloud — through the powerful Splunk backend, behind a friendly Laravel layer that lifts the burden of writing advanced SPL queries.

The challenge

  • Unify the analyst experience across heterogeneous log sources and formats.
  • Slash mean-time-to-respond (MTTR) with rich keyword and time-range search.
  • Persist investigation results for historical analysis, audit, and compliance.
  • Provide a console approachable to analysts without deep SPL expertise.

What we built

  • An ingestion layer that pushes events into Splunk through the HTTP Event Collector (HEC).
  • A custom search engine that compiles UI filters into optimised SPL queries on the fly.
  • Persistent investigation storage with PDF/CSV export.
  • Fine-grained RBAC scoped to source and index, per analyst.
Outcome: average incident-investigation time dropped from 45 min to under 8 min, with full audit history of every search.

Highlight features

  1. Multi-source log ingestion (JSON, Syslog, CSV, Apache/Nginx).
  2. Rich search by keyword, time range and severity level.
  3. Persistent saved searches with replay-on-demand.
  4. Visual dashboards summarising incidents and critical alerts.
  5. Webhook alerts to Slack and Microsoft Teams.

Classification: defensive cybersecurity — Blue Team — Splunk tooling. Engineered with discipline by the Smart Lead Tech team.

Tech stack

What powers this product — the core frameworks and the full stack behind it.

Core stack

  • Laravel

Also in the stack

  • PHP
  • Splunk Enterprise
  • HEC
  • MySQL
  • Redis

Screens

Splunk Log Viewer dashboard — security log analysis — 1
1 / 4

Related projects

  • CybersecurityLaravel

    Security Guard Scanner — Automated Web Vulnerability Scanner

    An end-to-end web vulnerability scanner that detects XSS, SQLi, CSRF and server-side weaknesses automatically — with downloadable, audit-ready reports.

    Show more
    Security Guard Scanner — automated vulnerability report
  • CybersecurityNext.js

    CyberBattleGround — Capture-The-Flag Platform

    A full Capture-The-Flag arena for training cybersecurity teams and stress-testing vulnerability-discovery skills inside an isolated virtual environment.

    Show more
    CyberBattleGround security platform — live leaderboard